Chinese-linked LightSpy spyware targets South Asian iPhones
Network safety specialists have found a “recharged” digital surveillance crusade focusing on clients in South Asia fully intent on conveying an Apple iOS spyware embed called LightSpy.
“The most recent cycle of LightSpy, named ‘F_Warehouse,’ flaunts a measured system with broad spying highlights,” the BlackBerry Danger Exploration and Knowledge Group said in a report distributed the week before.
There is proof to recommend that the mission might have designated India in light of VirusTotal entries from inside its nation.
First recorded in 2020 by Pattern Miniature and Kaspersky, LightSpy alludes to a high level iOS secondary passage that is circulated by means of watering opening assaults through compromised news destinations.
A resulting examination from ThreatFabric in October 2023 revealed framework and usefulness covers between the malware and an Android spyware known as DragonEgg, which is credited to the Chinese country state bunch APT41 (also known as Winnti).
The underlying interruption vector is by and by not known, despite the fact that it’s thought to be by means of information sites that have been penetrated and are known to be visited by the objectives consistently.
The beginning stage is a first-stage loader that goes about as a platform for the center LightSpy secondary passage and its various modules that are recovered from a distant server to pull off the information gathering capabilities.
LightSpy is both completely highlighted and particular, permitting danger entertainers to gather delicate data, including contacts, SMS messages, exact area information and sound accounts during VoIP calls.
The most recent rendition found by the Canadian network safety firm further develops its abilities to take records along with information from well known applications like Wire, QQ, and WeChat, iCloud Keychain information, and internet browser history from Safari and Google Chrome.
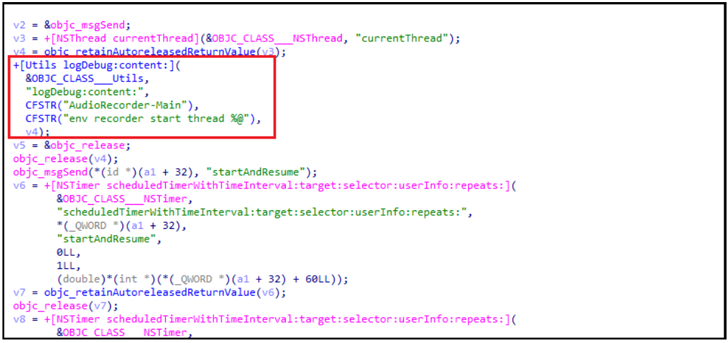
The mind boggling surveillance system likewise includes capacities to accumulate a rundown of associated Wi-Fi organizations, insights concerning introduced applications, take pictures utilizing the gadget’s camera, record sound, and execute shell orders got from the server, probable empowering it to capture control of the contaminated gadgets.
“LightSpy utilizes declaration sticking to forestall identification and interference of correspondence with its order and-control (C2) server,” Blackberry said. “Hence, on the off chance that the casualty is on an organization where traffic is being dissected, no association with the C2 server will be laid out.”
A further assessment of the embed’s source code proposes the contribution of local Chinese speakers, raising the chance of state-supported action. Likewise, LightSpy speaks with a server situated at 103.27[.]109[.]217, which additionally has a head board that shows a blunder message in Chinese while entering erroneous login qualifications.
The improvement comes as Apple said it conveyed danger notices to clients in 92 nations, counting India, that they might have been designated by hired soldier spyware assaults.
“The arrival of LightSpy, presently furnished with the adaptable ‘F_Warehouse’ structure, flags a heightening in versatile secret activities dangers,” BlackBerry said.
“The extended capacities of the malware, including broad information exfiltration, sound reconnaissance, and potential full gadget control, represent a serious gamble to designated people and associations in Southern Asia.”