Unpatched Lighttpd flaw found in Intel and Lenovo BMCs
A security imperfection affecting the Lighttpd web server utilized in baseboard the board regulators (BMCs) has remained unpatched by gadget sellers like Intel and Lenovo, new discoveries from Binarly uncover.
While the first deficiency was found and fixed by the Lighttpd maintainers way back in August 2018 with form 1.4.51, the absence of a CVE identifier or a warning implied that it was ignored by designers of AMI MegaRAC BMC, eventually winding up in items made by Intel and Lenovo.
Lighttpd (articulated “Lighty”) is an open-source superior execution web server programming intended for speed, security, and adaptability, while upgraded for elite execution conditions without consuming a ton of framework assets.
The quiet fix for Lighttpd concerns a too far out read weakness that could be taken advantage of to exfiltrate delicate information, for example, process memory addresses, accordingly permitting danger entertainers to sidestep critical security components like location space design randomization (ASLR).
“The shortfall of brief and significant data about security fixes forestalls legitimate treatment of these fixes down both the firmware and programming supply chains,” the firmware security organization said.
The imperfections are portrayed underneath :
- Beyond the field of play read in Lighttpd 1.4.45 utilized in Intel M70KLP series firmware
- Too far out read in Lighttpd 1.4.35 utilized in Lenovo BMC firmware
- Beyond the field of play read in Lighttpd before 1.4.51
Intel and Lenovo have selected not to resolve the issue as the items integrating the powerless rendition of Lighttpd have hit finish of-life (EoL) status and are at this point not qualified for security refreshes, successfully transforming it into an eternity day bug.
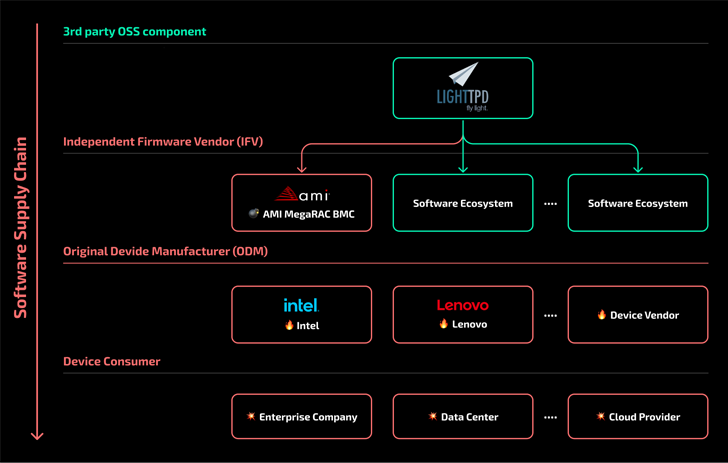
The divulgence features how the presence of obsolete outsider parts in the most recent adaptation of firmware can navigate the production network and posture accidental security takes a chance for end clients.
“This is one more weakness that will stay unfixed everlastingly in certain items and will introduce high-influence hazard to the business for quite a while,” Binarly added.